
Federal
ATO, FedRAMP 20x,
800-53, 800-171, CMMC.
The same record, in the shape your program office expects. One implementation record, hash chained inside your tenant, projects into every artifact indexed below.
In one paragraph
Every artifact indexed here is a projection of one hash-chained record inside your tenant. SSP, POA&M, and SAR generate from that record and export as OSCAL 1.1.2; SPRS-relevant evidence for the 110 requirements of NIST 800-171 and continuous authorization records are the same rows in a different envelope. PolicyCortex is not a C3PAO and does not certify anything.
How this page relates to the proofs
Everything below is a projection of three records: proof of state (what your cloud was, as of any timestamp), proof of change (what changed it, append only and hash chained), and proof of agency (what your machines were allowed to do, and what they actually did).
The SSP, POA&M, and SAR are generated from that one implementation record, not written beside it. OSCAL 1.1.2 export, SPRS-relevant evidence for the 110 requirements of NIST 800-171, and continuous authorization records are the same rows in a different envelope. When a collector was down or a scope was unobserved, the projection says so: a declared gap with interval and reason, never silently fewer rows.
- NIST 800-53
- Control implementations traced to evidence rows; SSP and SAR generated, not authored.
- NIST 800-171
- All 110 requirements mapped, with SPRS-relevant evidence carried per requirement.
- CMMC Level 2
- Assessment objectives linked to rows a C3PAO can verify by hash.
- FedRAMP 20x
- OSCAL 1.1.2 native; continuous authorization as machine-readable records.
- MITRE ATT&CK / ATLAS
- Techniques annotated on detections and agent actions, including AML.T0048 and AML.T0051.
- NIST AI RMF
- GOVERN, MAP, MEASURE, MANAGE tied to the proof of agency record.
ATO and continuous authorization
An authorization decision is a claim about a system as of a date. The record regenerates to any historical timestamp, so the package your authorizing official signed and the package you hold today differ only by rows you can enumerate. Chain verification tells both of you whether anything was edited after the fact.
- platform.ato
- ATO and continuous authorization: SSP, POA&M, and SAR generated from one implementation record, regenerable as of any timestamp.
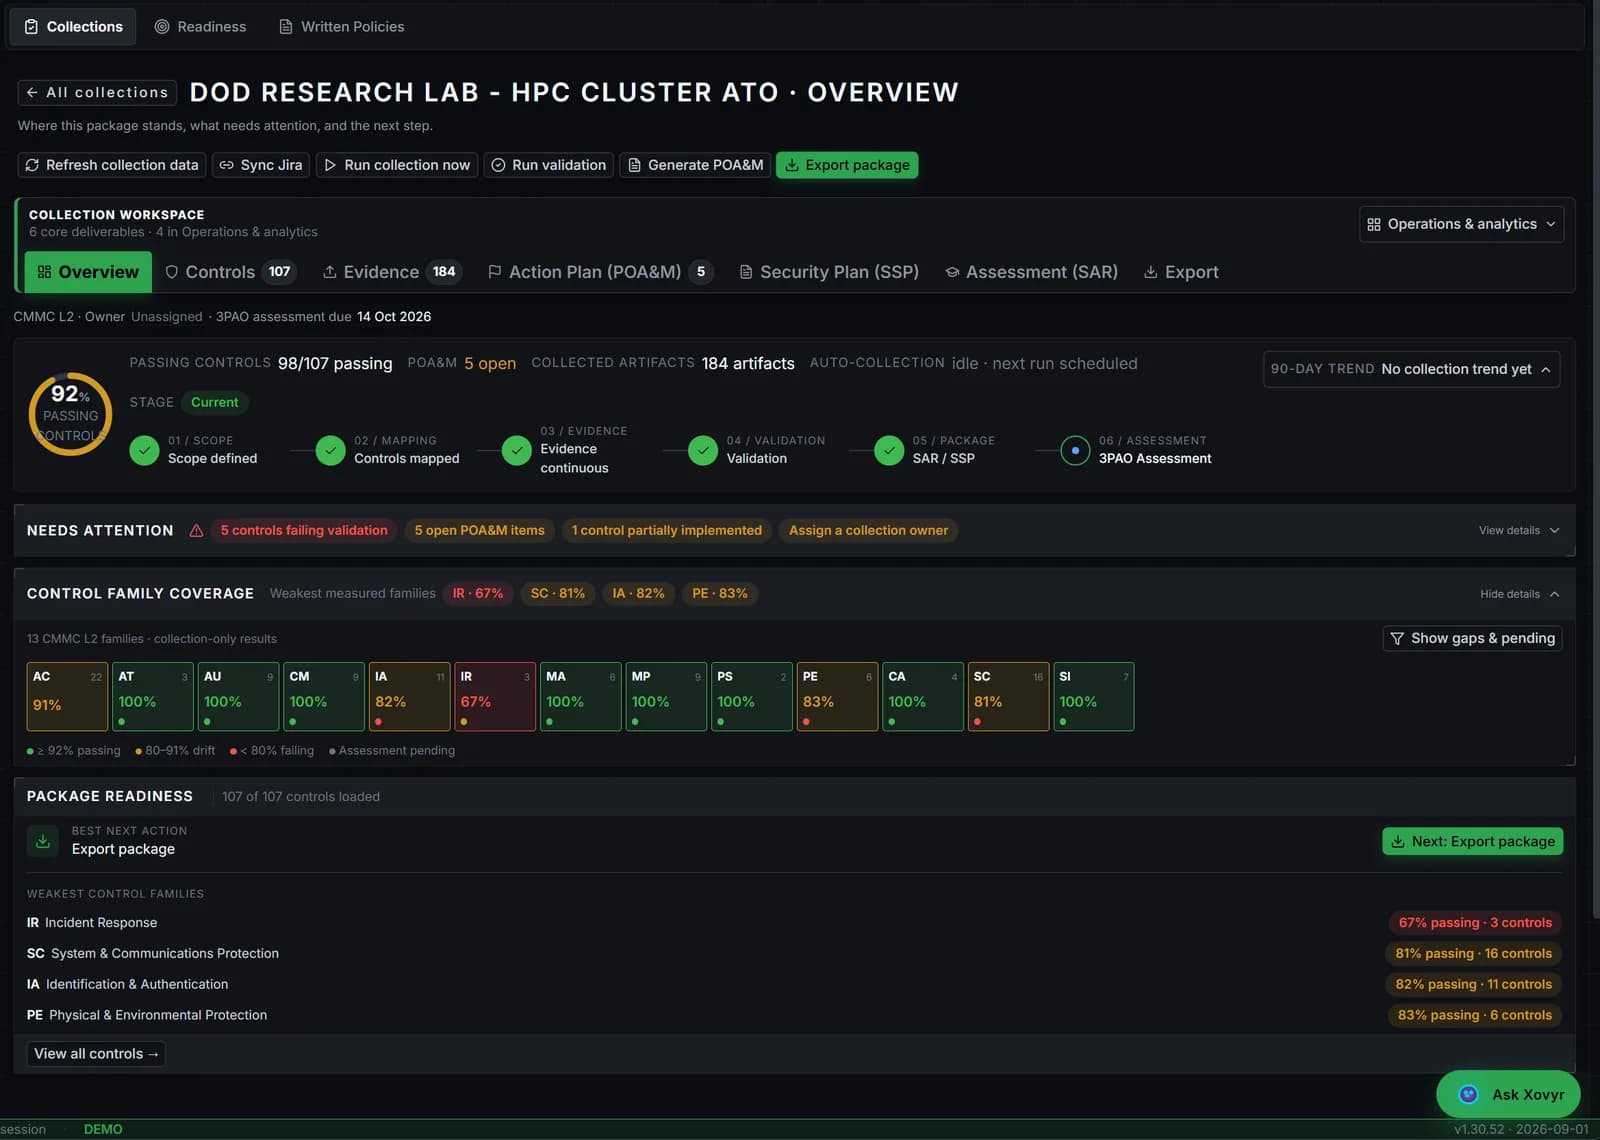
Governance and compliance monitoring
Monitoring against NIST 800-53, NIST 800-171, and CIS benchmarks, written as evidence: every observation content hashed with SHA3-256, timestamped, appended to the chain, retained seven years. A control that stopped being observed produces a declared gap, not a stale green.
- platform.governance
- Governance and compliance monitoring: 800-53, 800-171, and CIS, recorded as chained evidence inside your tenant.
CMMC Level 2
CMMC Level 2 assesses the 110 requirements of NIST 800-171. Start with the public ten-question readiness assessment, which runs in your browser without an account or cloud connection. Work the 110-control checklist requirement by requirement, then review how an evidence package is prepared for the assessor. Product access requires a separate request and review.
- cmmc.assessment
- Public CMMC Level 2 readiness assessment: ten questions in your browser, with no account or cloud connection required.
- cmmc.checklist
- The 110-control checklist: every requirement, the evidence it wants, and where that evidence comes from.
- cmmc.handoff
- eMASS and C3PAO handoff package: what the assessor receives and how they verify it by hash.
- cmmc.glossary
- The glossary: terms as assessors use them, not as vendors do.
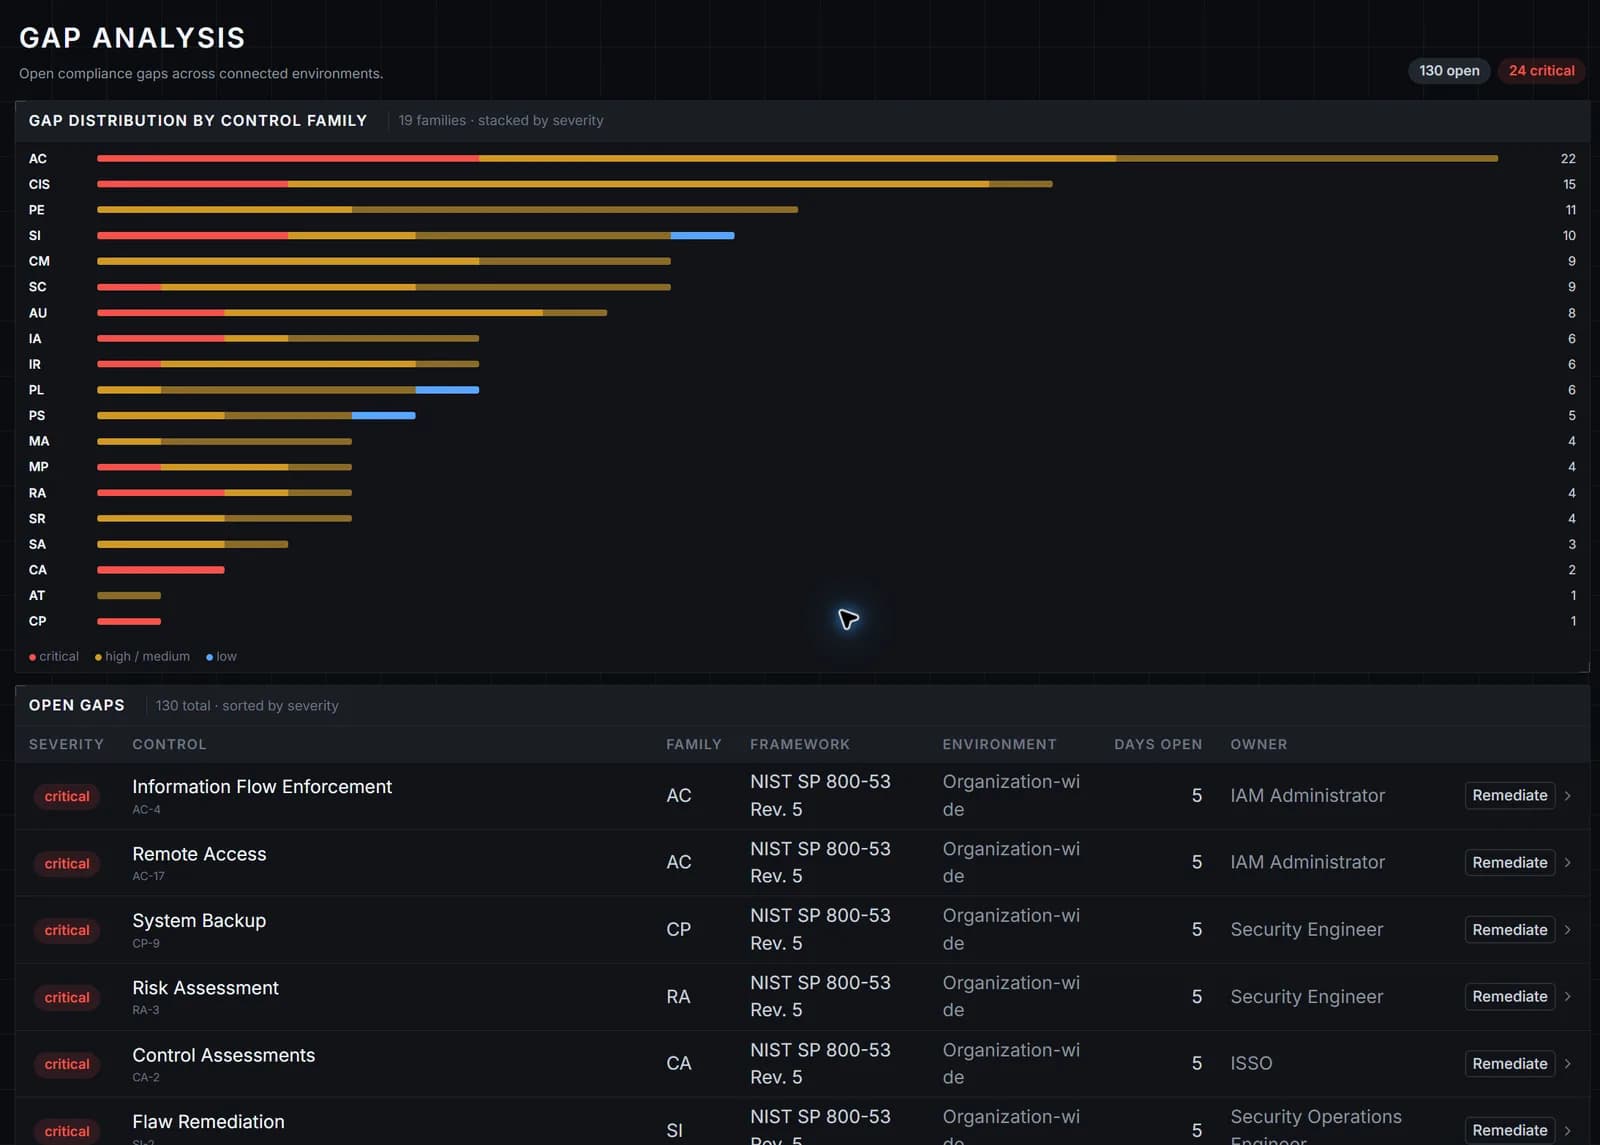
Calculators and tools
Two questions a program office asks early: what will this cost, and how much calendar remains. The calculators exist so both answers arrive before the first conversation.
- tools.cost
- CMMC cost calculator: an estimate you can argue with, line by line.
- tools.deadline
- CMMC deadline calculator: the calendar between today and your clause.
- tools.index
- All calculators and tools: the full set.
Framework solution briefs
One brief per framework or mission context: what the record contributes to that obligation, and what remains yours to do.
- brief.cmmc
- CMMC compliance: Level 2, from scoping to assessment day.
- brief.nist-800-171
- NIST 800-171: the 110 requirements and the evidence each one wants.
- brief.fedramp
- FedRAMP: 20x and continuous authorization as machine-readable records.
- brief.dfars
- DFARS compliance: 252.204-7012 obligations and the flowdown.
- brief.itar
- ITAR compliance: export-controlled data boundaries and evidence of enforcement.
- brief.defense
- Defense contractors: prime and subcontractor evidence posture.
- brief.federal-rd
- Federal R&D: labs and research computing under federal data obligations.
The engagement and procurement
If you want the record stood up for you, the delivery engagement is 30 days at a fixed fee, run on the same software indexed on this page. The procurement facts your contracting office asks for are published, not emailed on request.
- engagement
- The delivery engagement: 30 days, fixed fee, one agreed environment.
- procurement
- Procurement facts: PolicyCortex, Inc. SAM active. CAGE 19CQ3. Dallas-Fort Worth, Texas.
The delivery engine
The pages above describe outputs. The software that produces them runs inside your tenant with no telemetry pipeline back to PolicyCortex, and every autonomous action is bounded by an envelope: blast radius, cost ceiling, change windows, an andon cord. The delivery team uses the same software; there is no internal edition.
- platform
- The delivery engine: the software the delivery team uses.
What this page is not
Bring your program office. We speak OSCAL.
Request Access