Purpose-built for government. Not just another SaaS.

PolicyCortex collects compliance evidence inside your own cloud boundary and builds your SSP, POA&M and assessment package from it, for NIST 800-53 and 800-171, CMMC and continuous ATO. Your assessor or authorizing official can check every record without taking our word for it.

A person replies within one business day. Nothing connects to your environment until you agree on a read-only scope.

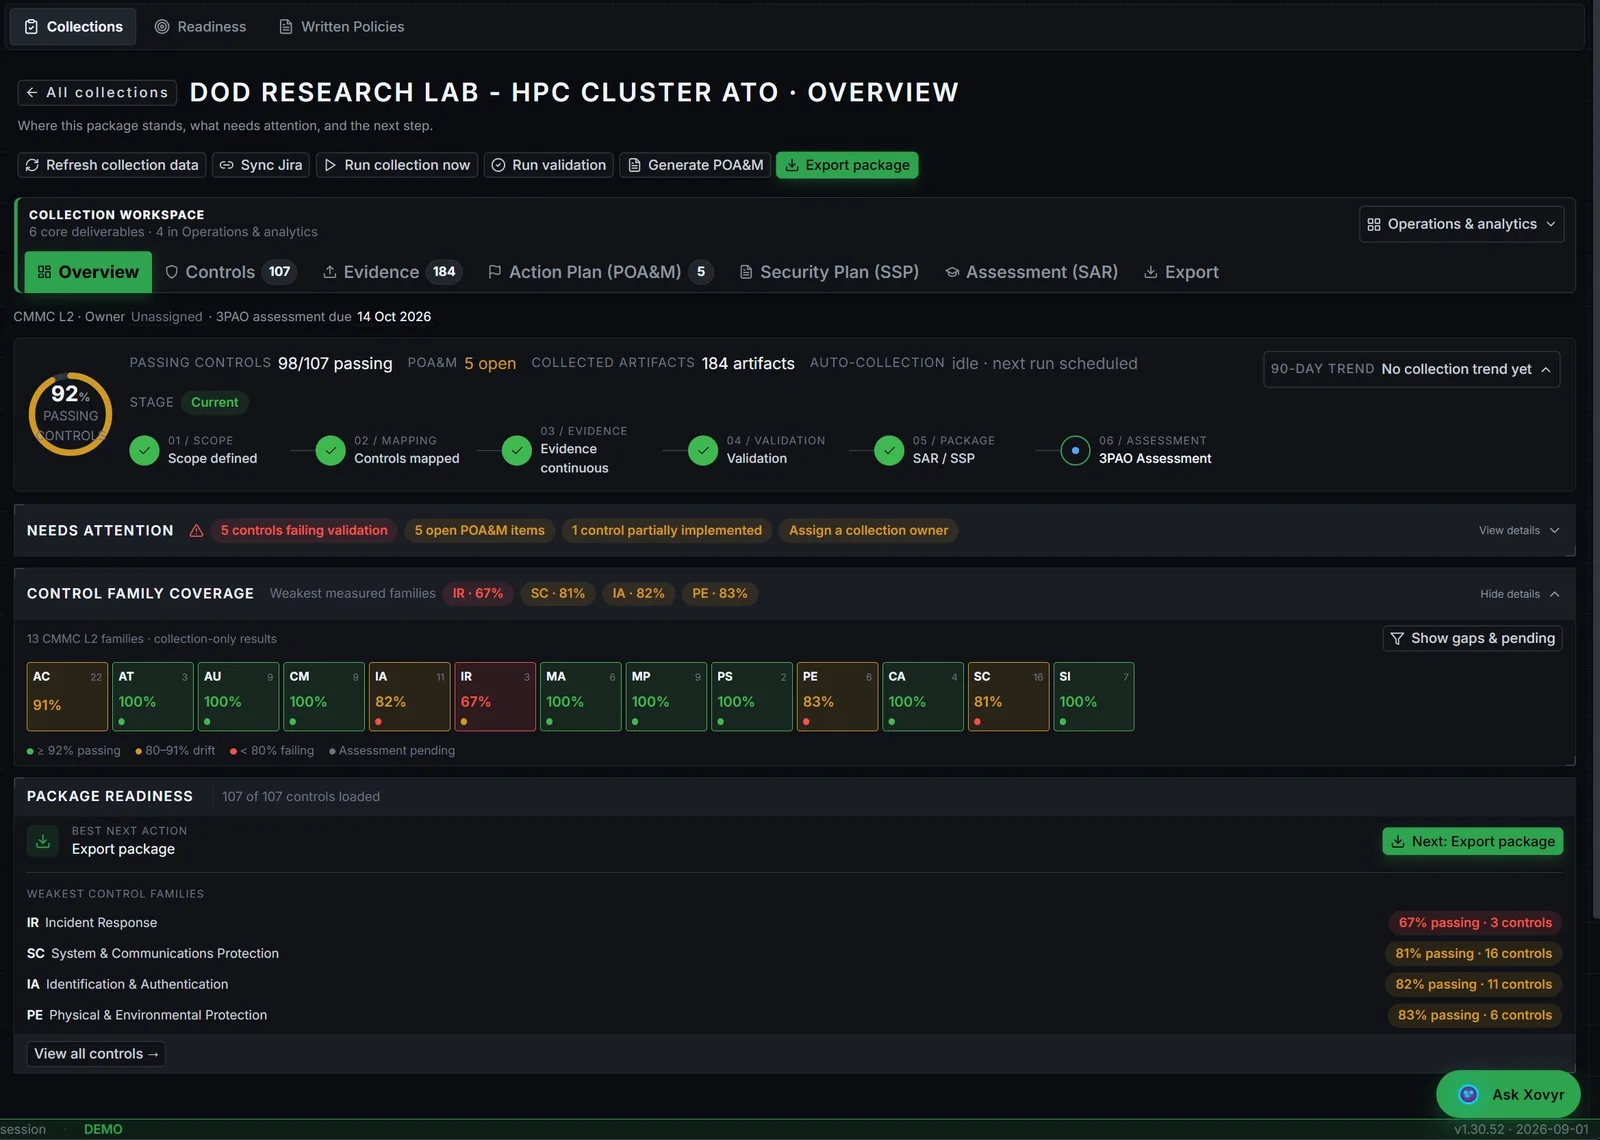
PolicyCortex collection workspace for one authorization package: 92 percent of controls passing, lifecycle from scope to assessment, control family coverage and package readiness
The product, shown with illustrative demo data.

Run it in your own Azure Government or Azure commercial subscription, on your own Kubernetes cluster, or on the hosted service. It supports Azure Government, AWS GovCloud (US) and GCC High.

Our mission is to give government programs, and the companies that serve them, a record of their controls, changes and automated actions that an assessor or authorizing official can check for themselves, without taking anyone's word for it, ours included.

  • CMMC Level 2
  • NIST SP 800-171
  • NIST SP 800-53
  • FedRAMP 20x
  • OMB M-25-21

The Platform

From live cloud state to an assessor-ready package.

Five-state control readiness, owned remediation lineage, and one-click SSP, POA&M, SAR, and OSCAL 1.1.2 exports. In a customer-operated installation they are generated inside your own cloud boundary, with no telemetry to PolicyCortex.

  • Continuous control readiness: Live evaluation and cryptographic sealing across every connected resource.
  • In your boundary: Available as a customer-operated installation in your own Azure Government or Azure commercial subscription or on your own Kubernetes cluster, delivered with our engineers. Supports AWS GovCloud (US) and GCC High.
  • Recomputable package: Assessors verify the evidence stream in the exported package offline.
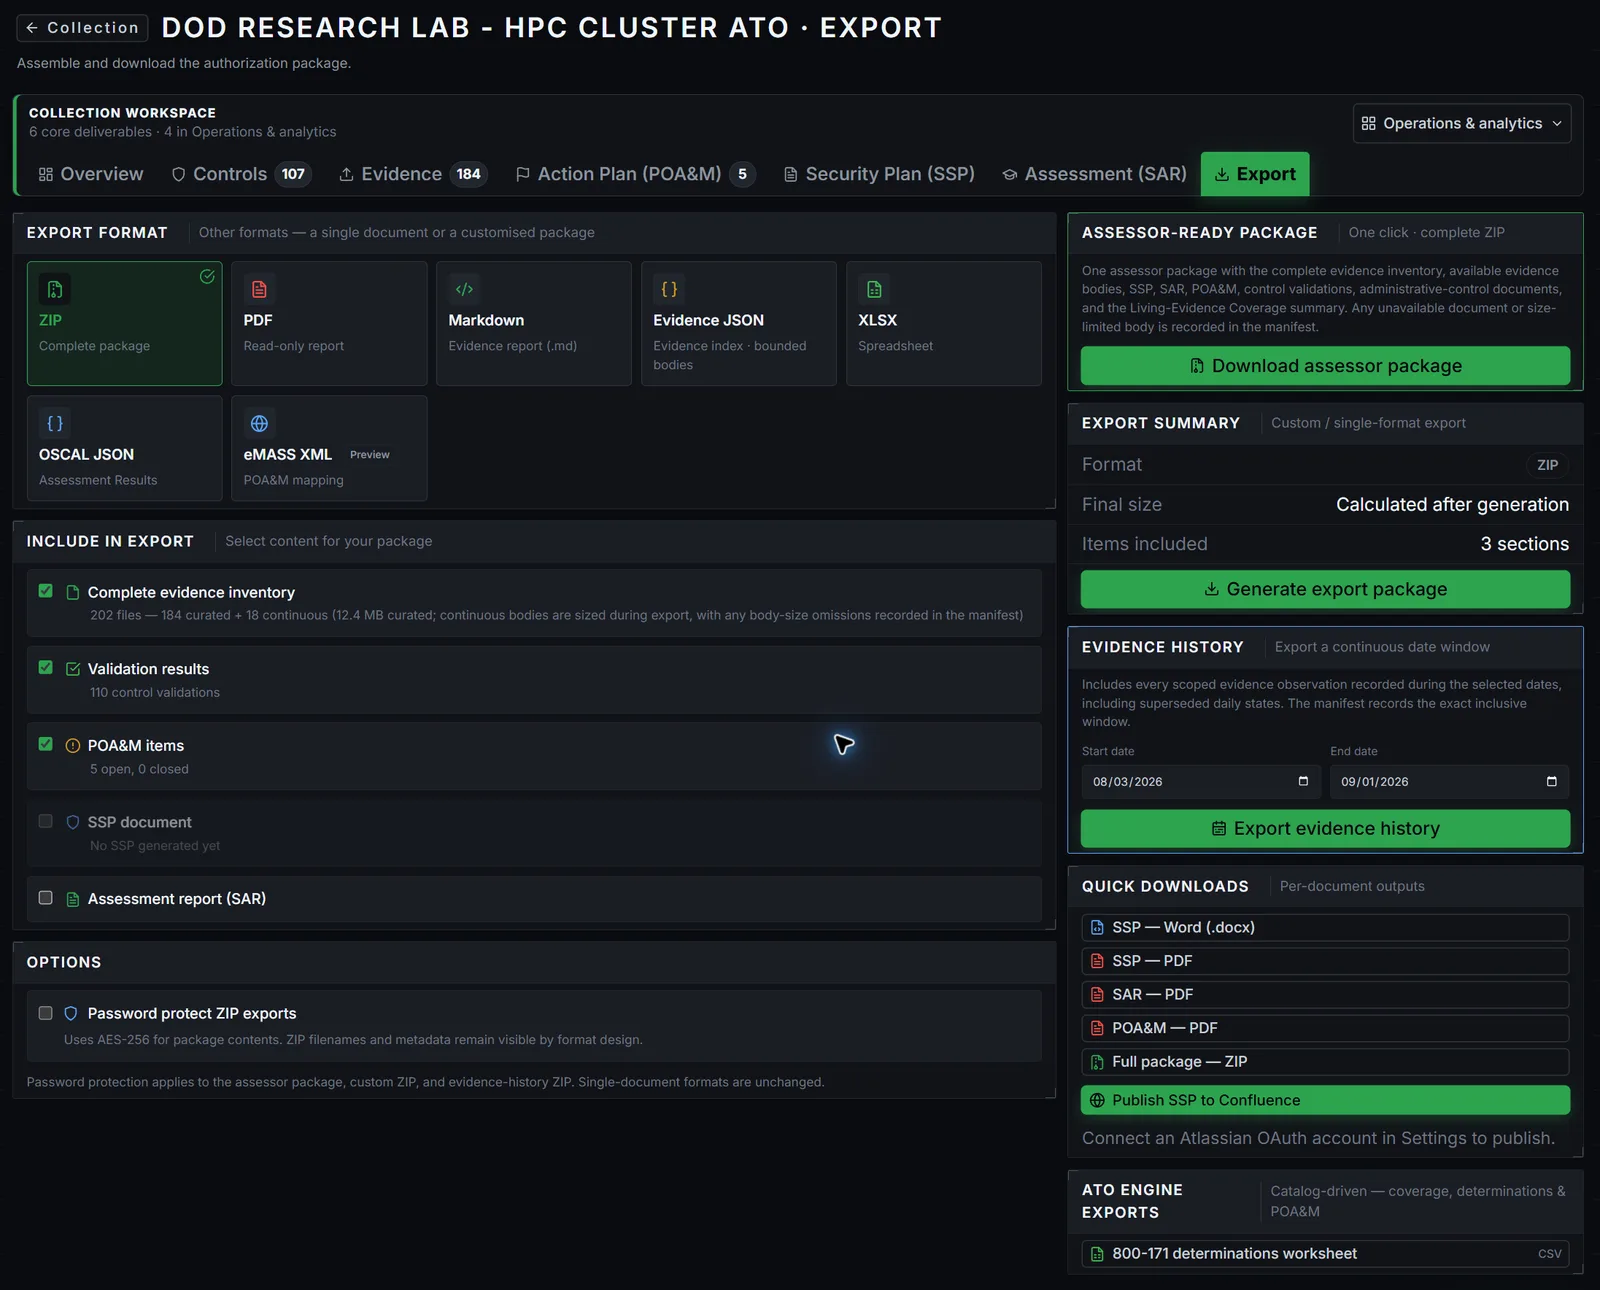
PolicyCortex assessor package export showing SSP, POA&M, SAR, and OSCAL 1.1.2 deliverables
National Security Agency headquarters campus at Fort Meade
01 · Your boundary

Runs where your system runs

In a customer-operated installation, delivered with our engineers, collectors, the policy engine and the evidence store run inside your own Azure Government or Azure commercial subscription, or on your own Kubernetes cluster. They support Azure Government, AWS GovCloud (US) and GCC High, and your evidence stays in your boundary.

Aerial view of the Pentagon headquarters
02 · Federal authorization

One record for every framework you answer to

One evidence record maps to NIST 800-53 Rev. 5 at the Low, Moderate and High baselines (the basis of the FedRAMP baselines), NIST 800-171 Rev. 2 and CMMC Level 2, and exports OSCAL 1.1.2 for FedRAMP 20x.

Blast-hardened access tunnel inside Cheyenne Mountain Complex
03 · Assessor handoff

Your assessor checks it offline

3PAO and C3PAO assessors receive your exported SSP, POA&M, SAR and OSCAL 1.1.2 bundle and verify its evidence stream offline, with no PolicyCortex account.

Get started

See where your program stands.

Bring your framework, system scope and current gaps. We will map the path to a review-ready package, starting with a read-only verification in your own environment.