
NIST SP 800-53 Rev 5 / OSCAL 1.1.2 / customer-operated installation
Continuous ATO for federally funded research.
FFRDCs, national laboratories, and university-affiliated research programs run on perpetual authorization cycles. PolicyCortex records every NIST SP 800-53 Rev 5 control implementation in the boundary as hash-chained evidence, generates the SSP, POA&M, and SAR from that record, and exports OSCAL 1.1.2. For an enclave it is available as a customer-operated installation, delivered with our engineers.
A person replies within one business day. Scope and onboarding are agreed with your team.
Five-State LedgerFederal R&D
Every scope state accounted for
AC-2Account managementPassSC-28Protection at restPassCM-6Baseline configurationFailAU-9Unobserved scopeDeclared GapPE-3Facility boundaryStale / N-AWhat a research enclave's authorization asks you to prove
Research computing changes faster than an authorization package can be rewritten: new instruments, new collaborators, new data-use agreements, new hosts inside the boundary. The authorizing official still signs a claim about the system as of a date, and the SAR still has to describe what the assessor found rather than what the program remembers. Between re-authorizations the POA&M has to move with the environment, and every closure needs closure evidence.
Some enclaves are disconnected by design. The obligation does not change: the record has to be produced inside the enclave and carried out through an approved transfer, with its chain intact.
- rd.baseline
- NIST SP 800-53 Rev 5 at Low, Moderate, or High, with program overlays where the control selection is tailored.
- rd.package
- SSP, SAR, and POA&M generated from one implementation record; OSCAL 1.1.2 and the eMASS POA&M worksheet.
- rd.enclave
- Available as a customer-operated installation, delivered with our engineers. The Kubernetes installation is documented for an offline image bundle; a disconnected cluster cannot collect from a cloud it cannot reach. Evidence is exported through your approved transfer mechanism.
- rd.people
- The founder holds active DoD Secret and DoE Q clearances and currently works in cloud security at a DOE national laboratory.
The evidence produced inside the enclave
The package is a projection of three records. Where each proof files under 800-53:
- CA-7 · CA-2 · CA-6
- Proof of state: continuous monitoring and re-authorization grounded in point-in-time records of every control implementation, regenerable to the date the authorizing official names.
- AU-9 · AU-10
- The exported chain: an audit record whose later modification is detectable, retained seven years on the hosted service.
- CM-3 · CM-8
- Proof of change and the system inventory: a new host, instrument, or collaborator account is a row with actor, authority, and timestamp, not a surprise at the next SAR.
- AC-6 · SI-4
- Proof of agency: what autonomous tooling in the enclave was permitted to do before it ran, and what it did.
- SSP · SAR · POA&M
- Generated from one implementation record, exported as OSCAL 1.1.2. Assessors with OSCAL tooling consume it directly; everyone else gets the evidence package.
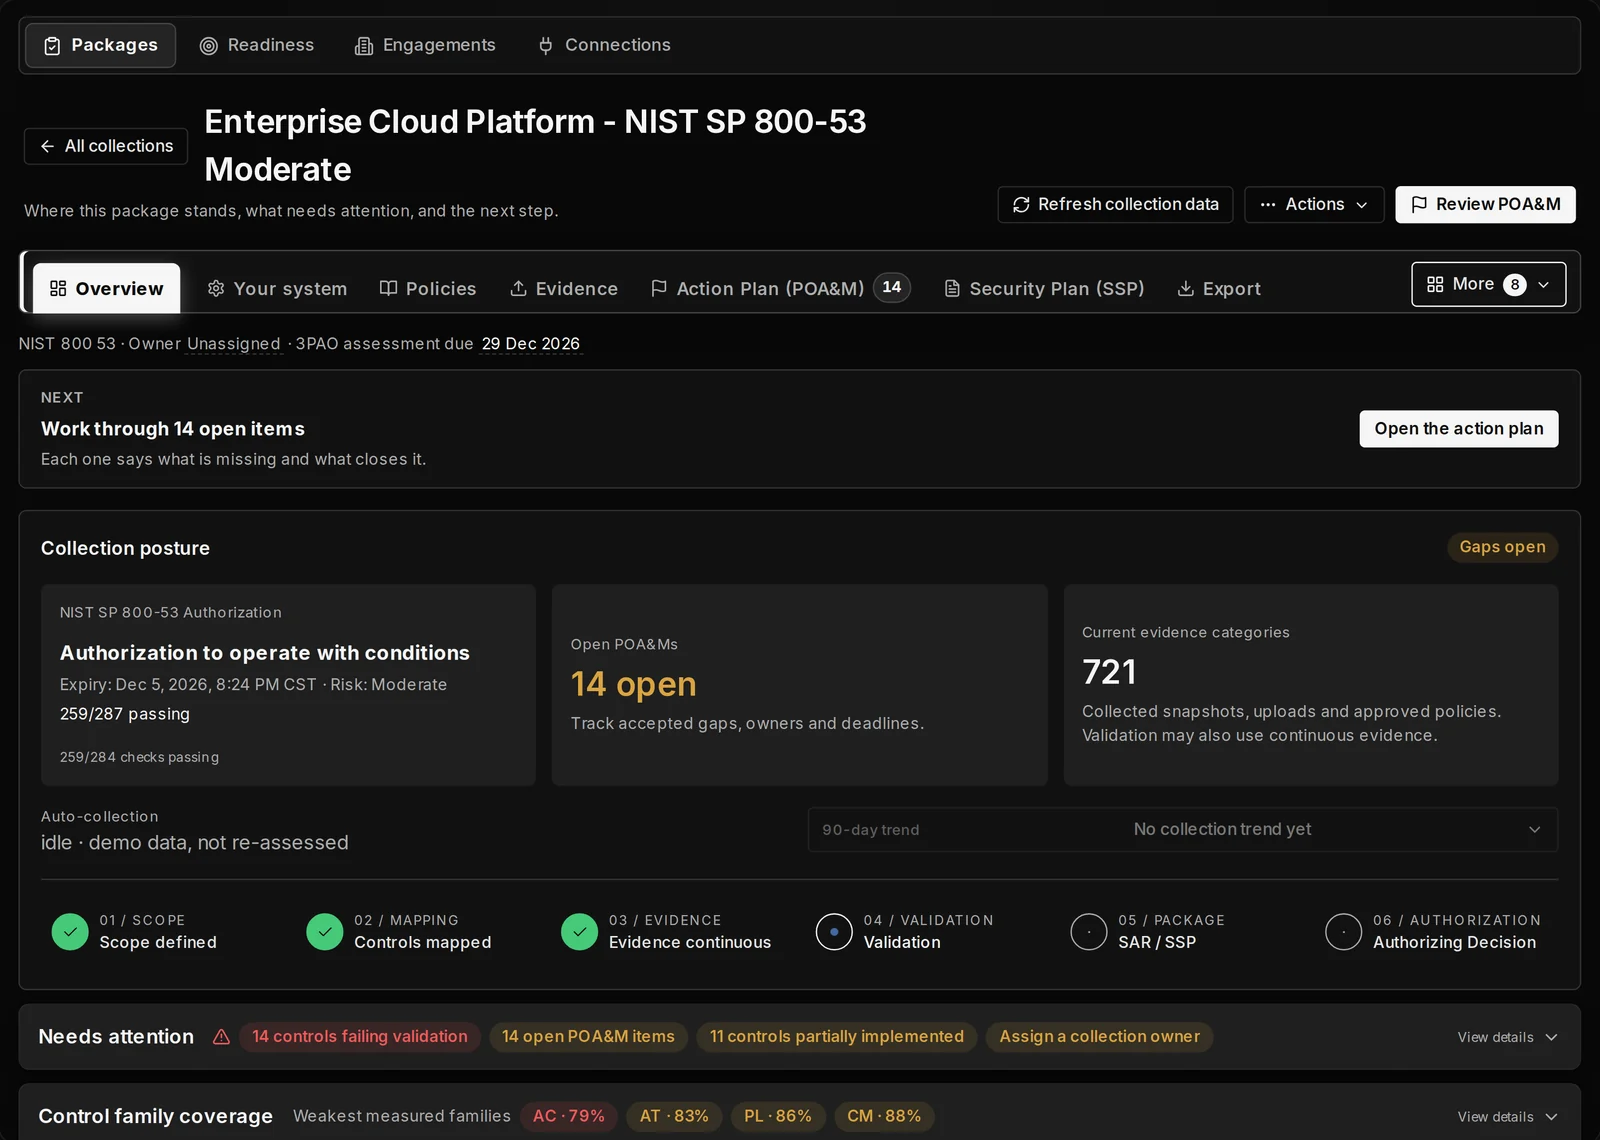
How the record is verified after transfer
For a disconnected enclave the recomputation happens on the receiving side: the evidence leaves through your approved transfer mechanism with its chain intact, and the assessor recomputes it there without a connection back to the enclave.
Access and onboarding in a research enclave
We agree on the enclave scope, impact level, overlays, and onboarding before access is granted. Read-only captures run against the connected enclave and file under the 800-53 families the SAR will cite.
- eval.mode
- SHADOW. Watch only; nothing executes.
- eval.onboarding
- A person replies within one business day. Scope and onboarding are agreed with your team.
- eval.location
- The hosted service, or a customer-operated installation delivered with our engineers. Azure, AWS, and GCP are observed clouds; AWS GovCloud (US), Azure Government, and GCC High are supported.
Delivery, if you want the record stood up for you
Licensing does not depend on it, but a fixed-scope delivery engagement is available: thirty days, one agreed primary cloud environment, an evidence package built and defended through assessor review. The independent assessor makes the certification decision. No certification is guaranteed.
Every engagement is delivered by the people who hold the clearances and wrote the code. Delivery inside a cleared or disconnected enclave is scoped with you before work begins.
- engagement.scope
- Thirty days. One agreed primary cloud environment.
- engagement.outcome
- An evidence package built and defended through assessor review.
- engagement.limit
- The independent assessor decides. No certification is guaranteed.
Questions assessors and buyers ask
Can assessors consume the OSCAL output?
Yes. SSP, POA&M, and SAR export in OSCAL 1.1.2. Assessors with OSCAL-aware tooling consume it directly; everyone else receives the evidence package.
Does it run in an air-gapped enclave?
In part. The Kubernetes installation is documented for loading from an offline image bundle and is delivered with our engineers; the Azure installation is not air-gapped, and a disconnected cluster cannot collect evidence from a cloud it cannot reach. Evidence is exported through your approved transfer mechanism, with the chain intact so the receiving side can recompute it.
What about framework overlays?
NIST SP 800-53 Rev 5 baselines with impact-level tailoring (Low, Moderate, High). Program overlays are supported when the control selection is tailored.
Who operates the platform?
Your team, inside your enclave. Where an engagement is delivered, it is delivered by the people who hold the clearances and wrote the code; there is no sales organization between you and them.
Does PolicyCortex make us compliant?
No. It produces the records compliance decisions rest on. The authorizing official, the C3PAO, or the accountable official makes the determination; PolicyCortex hands them evidence they can recompute instead of a narrative they have to believe.
What happens when a collector is down?
The chain carries a declared gap: the stream, the interval, the reason, and when it was declared. Evidence never silently has fewer rows.
Re-authorize from the record, not from memory.