
Sample package
A sample SSP, POA&M and OSCAL package you can check yourself.
This is a sample assessor package that PolicyCortex generated from fictional demonstration data, for an imaginary NIST SP 800-53 Moderate system. It holds the SSP, the SAR, the POA&M, the eMASS POA&M worksheet, OSCAL 1.1.2 files and an evidence stream with its offline verifier. Download it without signing up and check it yourself.
Download the files
Six files, 4.2 MB in all, and no form to fill in. The ZIP is the package. The other five let you read the SSP, the POA&M, the worksheet and the verifier before you unzip anything.
The downloads
| File | What it is | Size | SHA-256 |
|---|---|---|---|
| policycortex-sample-ato-package.zip | The package (ZIP)The assessor-ready package as the product exported it: 748 files, with the SSP, SAR, POA&M, eMASS worksheet, OSCAL 1.1.2 files, the evidence, and the evidence stream with its verifier. | 2.7 MB | 2f4bdf5a522ba447664d3e18d364a183a0deeffe76074376f575dd6888d98a24 |
| policycortex-sample-ssp.pdf | SSP (PDF)The System Security Plan as the product renders it to PDF, 86 pages. The package holds it in Word. | 1.4 MB | 09e0d6d5cee379c3d18c2e499b52fe7398f46b0ff3812b96704f4e4d5bd6796b |
| policycortex-sample-poam.pdf | POA&M (PDF)The Plan of Action and Milestones as the product renders it to PDF: 16 items, 14 unresolved, 7 pages. | 103.3 KB | 810e7d693cc83900ec39f1b20509421eb640d336f7af96d349b338cdd1e8407f |
| policycortex-sample-emass-poam.xlsx | eMASS POA&M worksheetThe POA&M in the eMASS worksheet layout. The same file as POAM/eMASS_POAM.xlsx in the package. | 9.8 KB | 68c338f52d0c783bea9fcb162b67c8818426668ebc069accfe2872e09756d444 |
| verify_ | Offline verifierThe verifier every package carries, the same file as Evidence_History/verify_ledger.py. Python 3.6 or newer, standard library only. | 17.1 KB | 2fc871f068e9d51a9610550cf4dd712880272ed83c297fad200ed3fc94328a98 |
| policycortex-sample-verifier-output.txt | Verifier outputWhat the verifier printed when we ran it on the package. | 960 bytes | e0076f4d90c273772287904daa6248a4b17c21584e6ae156cf809683d35748b0 |
To check a download, compute its SHA-256 and compare it with this table: sha256sum on Linux, shasum -a 256 on macOS, certutil -hashfile <file> SHA256 on Windows.
What is inside the package
748 files, 24.9 MB unpacked. The table lists the files a reviewer opens first; the folders under it hold the rest. manifest.v2.json gives the size and SHA-256 of every other file in the package.
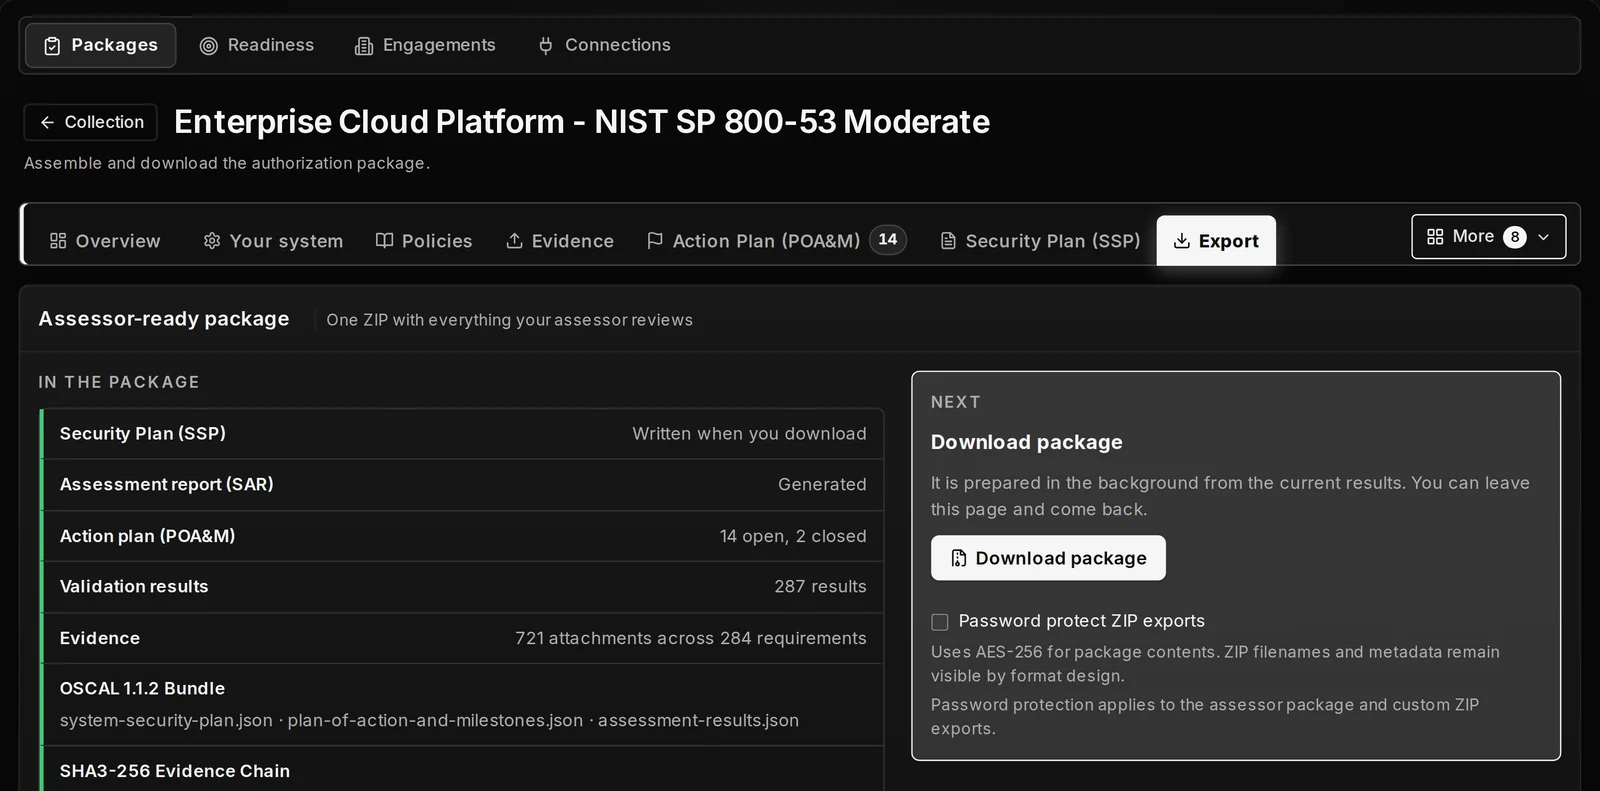
Inside the ZIP: the files a reviewer opens first
| Path | What it is | Size | SHA-256 |
|---|---|---|---|
| 00_ | Start here: the primary documents, in reading order. | 941 bytes | 94287bb7f969712b1d4e13c362f501fc130403852374127cc5a8c5b1de19f490 |
| README.txt | What each folder holds, and how to check every file against the manifest. | 2.8 KB | e9a9f3e06d066bd4b1a0c1685ecd3edc9541285a053e6cc3fadc81978a61e855 |
| SSP/ | System Security Plan, in Word. | 150.3 KB | a3cf6f20ce067623aba708464f6cab57744df7adc36cb2866a6f5871461ff06a |
| SAR/ | Security Assessment Report, in Word. | 71.0 KB | b03aeef921314572f0389276663a54f593d721931cad8107a48d093780546ef9 |
| POAM/ | POA&M in the eMASS worksheet layout, 16 items. | 9.8 KB | 68c338f52d0c783bea9fcb162b67c8818426668ebc069accfe2872e09756d444 |
| POAM/ | POA&M as JSON, 16 items with their milestones. | 20.7 KB | 86093044f0363bdc919e8cfc3c06a1d12a3b1f35fafbc7a439a79b9872ffe512 |
| OSCAL/ | OSCAL 1.1.2 System Security Plan. | 2.1 MB | baf3de1e2755061966e73de57effb12dbd11fc3a7a103d3f15c520b8f4d4bd0d |
| OSCAL/ | OSCAL 1.1.2 POA&M. | 1.1 MB | e49bb82e869c1cb9312254370752ba986aa14207bbeb4346b3a617028156d29b |
| OSCAL/ | OSCAL 1.1.2 assessment results. | 1.4 MB | 2e8407154e1721cfe15235a5197a479e520c75ee6ecc1316659dba191e413e1b |
| OSCAL/ | The three OSCAL documents in one file, with the UUIDs they share. | 10.7 MB | 1277783d82303102f98ce06e741234382cd20040712e229a2b26599595ebf22d |
| Evidence_ | The SHA3-256 evidence stream: 721 state captures, each chained to the one before. | 448.9 KB | 3fa59a465ab178486f09a7a28f38a942121a3a5953375438dc50fb57e7c093dd |
| Evidence_ | The stream's head digest and record counts, which the verifier checks the stream against. | 4.9 KB | 845b3c27b7f70c6c79d7c64a97f6b5a0948393add5883649b81d37931566df84 |
| Evidence_ | Declared collection gaps in the export window: none. | 306 bytes | 97a455838a24ed8d1cb0c8b62aca9f288ed42583e04ddf313e5ca7c2a650681e |
| Evidence_ | The offline verifier. | 17.1 KB | 2fc871f068e9d51a9610550cf4dd712880272ed83c297fad200ed3fc94328a98 |
| Evidence_ | How to run the verifier, or check the chain by hand. | 6.3 KB | 1ae05db78fb85b9697d07ae19e93d9de69587dd82de0a313b58dbbea73a0159e |
| Validation/ | One recorded result per control, 287 in all. | 140.8 KB | 2b98b4dc9ce8477d546e4bd2bb59abcc71fb91902bee940fc2191b345532635f |
| EVIDENCE_ | The controls with no evidence: AC-18 and two of its enhancements. | 1.1 KB | 9006d8087dfdf9f8c279c89f125bf749efbe4d8f6cf5779b9565374210041019 |
| manifest.json | Package summary: counts, gaps and coverage. | 673.8 KB | 61f41bd5d75a0f8d6bb5bc72d2a4cc99dfd74ff397be97f1e3075946ea232689 |
| manifest.v2.json | The size and SHA-256 of every other file in the package. | 918.4 KB | d37ff97ffb945a369f137378ee0c25aff59600a3e475a3a6c39b33681b6030b2 |
Inside the ZIP: the folders
| Folder | What it holds | Files | Size |
|---|---|---|---|
| Evidence/ | The attached evidence, one JSON record per item, filed by control family. At most five per control. | 721 | 875.7 KB |
| Formatted_ | The evidence report as Markdown, as JSON and as a Word-compatible document. | 3 | 6.3 MB |
| Review/ | Risk acceptance and STIG review context. None is recorded for this system. | 4 | 2.6 KB |
| Administrative_ | Approved policies and procedures. None is attached to this system. | 1 | 152 bytes |
Every file in these folders is listed with its SHA-256 in manifest.v2.json.
Check it yourself, offline
The verifier is one Python file. It needs Python 3.6 or newer and nothing else: no PolicyCortex account and no network.
- Unzip the package into an empty folder and open a terminal in it.
- Run the verifier. On Windows, type py instead of python3. The organization ID makes it also check that every record belongs to the organization the package names.
python3 Evidence_History/verify_ledger.py Evidence_History/ledger.jsonl --organization-id aa98488a-56df-457a-bb2c-e8c661543c04
- Compare what it prints with ours. status: INTACT means every record recomputes and links to the one before it; the line under the record counts says the stream matches ledger.json. Exit code 0 means both.
PolicyCortex evidence stream verification (SHA3-256)
stream: Evidence_History/ledger.jsonl
status: INTACT
headDigest: 9496e0defd46052a2285bfa9cdb68336eedb18f8ee6e622e8953caa690e866e9
records: 721 (state_capture 721, change_record 0, declared_gap 0, agency_record 0)
ledger.json: sha3Chain head digest and counts match
signature: ledger.json is not signed (UNSIGNED_NO_SERVER_KEY); keep the head digest outside PolicyCortex to detect later changes
not chained: 0 executed changes without an observed before and after state, 0 autonomous decisions without a recorded envelope evaluation (ids in manifest.json evidenceChainV2.exclusions)
- Then try to break it: in Evidence_History/ledger.jsonl, change one character of a record's controlId or contentHash and run it again. It reports BROKEN, names the first record that no longer recomputes, and exits with code 1.
- To check every other file, compare its SHA-256 with its entry in manifest.v2.json.
The stream's head digest is 9496e0defd46052a2285bfa9cdb68336eedb18f8ee6e622e8953caa690e866e9. This page keeps that value outside the package, so a copy whose records were changed and then re-hashed from end to end shows a different head.
What this sample is, and is not
- Data
- Fictional. The system, the organization, its cloud resources and their IDs come from the product's demonstration data. No customer cloud was scanned to make it.
- How it was made
- On November 10, 2026 a local copy of the application, built from the product's main branch, exported the package and the two PDFs from its own Export page. Nothing in them was edited; the files were only renamed. The worksheet and the verifier are copied out of the ZIP, and the verifier output is what the verifier printed.
- Signature
- Not signed. The local copy had no signing key, and the verifier's output says so. With a signing key set, a package also carries an HMAC-SHA256 signature that binds the stream's head digest and record counts, which the verifier checks when it is given the key.
- Evidence stream
- 721 state captures. The export found no executed changes, autonomous decisions or collection gaps for this system in its window, so the stream holds no change records, agency records or declared gaps.
- OSCAL
- Checked on November 10, 2026 against NIST's OSCAL 1.1.2 JSON schemas: the SSP, the POA&M and the assessment results all pass. The schemas check structure only; the further rules NIST's oscal-cli applies were not run.
- Assessment
- PolicyCortex prepares the record. It is not an assessor, and this sample is not an assessment or an authorization.
When the next sample is published
Optional, and not needed for the download. Leave a work email and we will write when a new sample is published.
Your own package
A package for your own system comes from the product once access is agreed. We review your environment first, and nothing connects to it until you agree on a read-only scope. Request Access.
Questions about the sample
- Q-01
Is any of this real customer data?
No. The product generated it from its demonstration data, which describes a fictional system at a fictional organization. No customer cloud was scanned to make it.
- Q-02
Do I need an account, or PolicyCortex installed, to verify it?
No. The verifier is one Python file that uses the standard library only. It runs offline, with no PolicyCortex account and no network.
- Q-03
What does a passing check prove?
That every record in the evidence stream still recomputes, in order, and that the stream matches ledger.json. Matching the head digest with a copy kept elsewhere, like the one on this page, rules out a stream rewritten from end to end. It does not show that the evidence was right when it was collected; the assessor examines that.
- Q-04
Can I get a package like this for my own system?
Yes, from the product, once access is agreed. Request access and we review your environment and agree a read-only scope before anything connects.
 YOUR BOUNDARY · CUSTOMER-OPERATED INSTALLATION
 SHA3-256 EVIDENCE STREAM · OFFLINE VERIFIER
A sample shows the format. Your package shows your system.