ResourcesBlog
Veeam Backup Flaw Lets an Attacker Bypass Authorization
Veeam fixes a 9.1 authorization bypass in Backup and Replication 13. Patch to a fixed build and record the build number.
Leonard EsereReading time 4 min
Filed underVeeamauthorization bypassflaw remediationbackupevidence
- Veeam fixes a 9.1 authorization bypass in Backup and Replication 13.
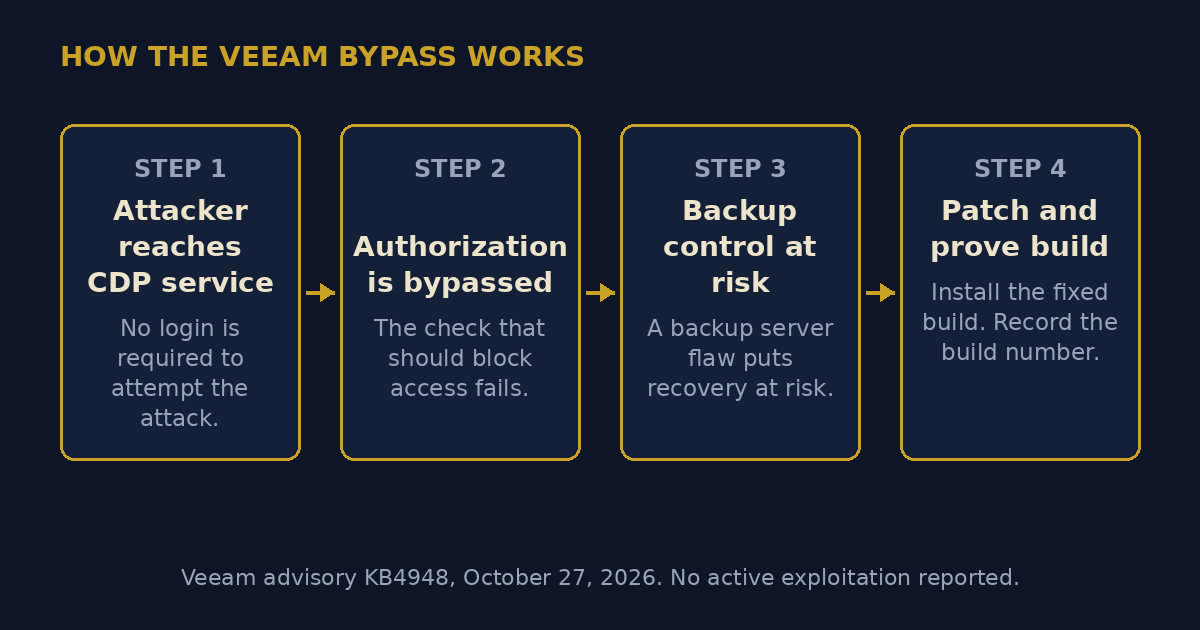
- An unauthenticated attacker can bypass authorization on the Continuous Data Protection (CDP) Coordinator Service.
- Fixed builds are 13.1.2 and 13.0.3, with exact build numbers in the article.
- Version 12.x is not affected, and no active exploitation is reported.
What Veeam published
Veeam published security advisory KB4948 on October 27, 2026. The advisory covers a critical flaw in Veeam Backup and Replication. The record is CVE-2026-108142. Common Vulnerabilities and Exposures (CVE) is the record system for public flaws. The score is 9.1 under Common Vulnerability Scoring System (CVSS) version 4.0. HackerOne serves as the CVE Numbering Authority (CNA) for this record. The weakness type is Common Weakness Enumeration (CWE) 636. The vector is AV:N/AC:L/AT:P/PR:N/UI:N/VC:N/VI:H/VA:H/SC:N/SI:H/SA:H.
What the flaw does
The service is the Continuous Data Protection (CDP) Coordinator Service. An unauthenticated attacker can bypass authorization on the CDP Coordinator Service. Unauthenticated means the attacker needs no login first. The flaw affects Windows deployments and the Veeam Software Appliance.
What is not reported
The advisory does not report active exploitation for this flaw. Do not treat a high score as proof of attacks in the wild. The case for acting now is the 9.1 score in a backup platform.
What to patch
- 13.1 line: builds up to and including 13.1.1.18 are affected.
- 13.1 fix: use 13.1.2, build 13.1.2.57.
- 13.0 line: builds up to and including 13.0.2.29 are affected.
- 13.0 fix: use 13.0.3, build 13.0.3.63.
- Version 12.x is not affected.
- Check the build number after install, not only the version line.
- A version number that looks close is not proof.
The governance lesson
Backup servers hold copies of everything else. A flaw in the backup platform puts recovery itself at risk. Your inventory must list every backup server and its exact build. Your inventory must cover both Windows hosts and appliances. Record the build before and after each patch. Record the patch date and the scan result after the patch. A ticket marked done with no build number is a claim. PolicyCortex does not patch Veeam. PolicyCortex helps teams link proof to requirements.
Sources
- CVE-2026-108142 record, CVE Program, published October 27, 2026, score 9.1
- National Vulnerability Database (NVD) record for CVE-2026-108142
- Veeam advisory KB4948, published October 27, 2026
- Original diagram by PolicyCortex
Next step
Patch each backup server to a fixed build and record the build number.
- What does unauthenticated mean?
- It means the attacker needs no login first.
- Which builds are fixed?
- Use 13.1.2, build 13.1.2.57, or 13.0.3, build 13.0.3.63.
- Is version 12.x affected?
- No. Version 12.x is not affected.
- Is active exploitation reported?
- No. The advisory does not report active exploitation.
Related records
Guides and articles describe the work. The evidence that work produces is described in three proof pages and one architecture page.
- proof.state
- Proof of State. What the environment was, as of a date someone else picks: point-in-time records, content hashed and chained.
- proof.change
- Proof of Change. Who or what altered the environment, under what authority, with before and after state hashes.
- proof.agency
- Proof of Agency. What a machine was permitted to do before it acted, what it did, and what would have stopped it.
- architecture
- Architecture. How the chain is built and where it lives: inside your tenant, with no egress of evidence.
Further reading in this register
- Linux Kernel Fragnesia Flaw Joins the CISA Exploited ListCISA lists a Linux kernel flaw as exploited. It chains with PHP flaws to reach root. Patch, reboot, and prove the running version.
- Adobe Commerce Upload Flaw Joins the Exploited ListCISA added the Adobe Commerce upload flaw to its exploited list on October 27, 2026. Stores must patch to the July 2026 build and hunt for planted code.
- Jackson Databind 9.8 Flaw Bypasses Its Own Type CheckA new Jackson flaw scores 9.8. It bypasses a recent fix. Upgrade to a fixed build now.
Verify the record this entry describes.
- Published
- Last updated
- Unchanged since publication
- Author
- Leonard Esere